What this lab covered
How traffic can be intercepted on a local network. In an isolated lab with a Kali attacker and a Windows victim, I used bettercap (with Ettercap and Cain & Abel for comparison) to sit between the victim and the gateway and observe their traffic.
Steps
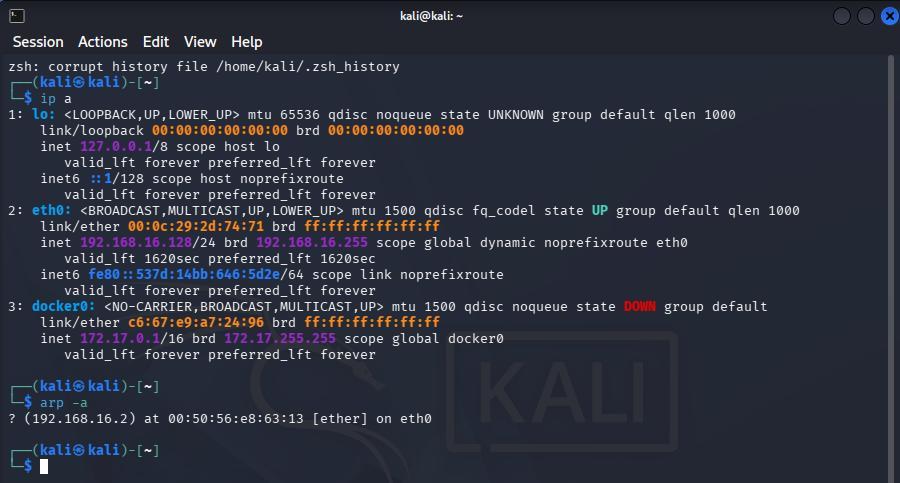
- Check the lab layout. Confirm the attacker, victim and gateway addresses on the same segment:
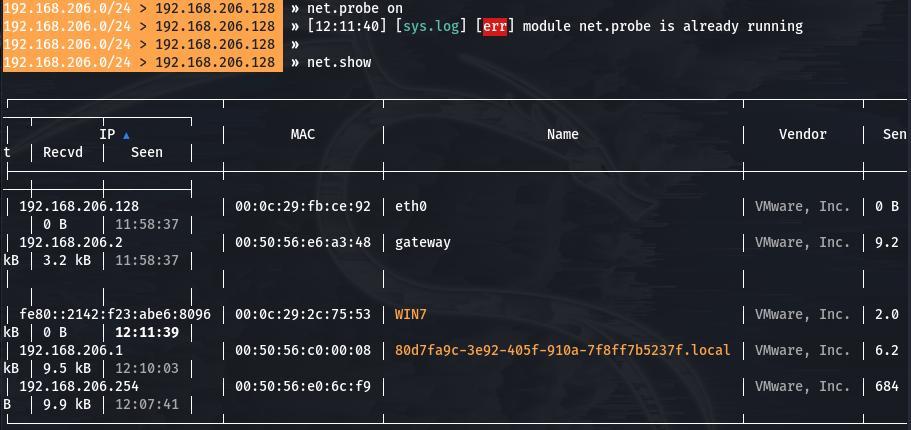
ip a arp -a - Start bettercap and discover hosts. Launch it on the LAN interface and probe the subnet to list live hosts, their MACs and the gateway.
- ARP spoof. Tell the victim that the attacker's MAC is the gateway, so their traffic flows through Kali first. Enable IP forwarding to stay transparent.
- (Optional) DNS spoof. Redirect a chosen domain to a page under your control.
- Sniff. Enable sniffing and wait — any credentials sent over plain HTTP appear in the bettercap log.
What I took from it
The whole attack depends on two weaknesses: ARP has no authentication, and the captured logins were only readable because they travelled over plain HTTP. Over HTTPS the same interception yields encrypted bytes, not passwords.
Defender's view
HTTPS everywhere (and HSTS) is the big one — it turns a captured session into useless ciphertext. On the network side, dynamic ARP inspection, DHCP snooping, port security and segmentation make the spoofing itself much harder, and arpwatch-style monitoring flags a gateway MAC that suddenly changes.