What this covered
A group assignment assessing OWASP Juice Shop, a deliberately vulnerable web app built for security training. We worked across three vulnerability classes from the OWASP Top 10.
Cross-Site Scripting (XSS)
XSS happens when user-controlled input is rendered as part of the page without being treated strictly as data, so the browser runs it as script. In Juice Shop, injecting markup into the search field executes it — a classic DOM XSS, confirmed with a harmless payload that pops an alert.
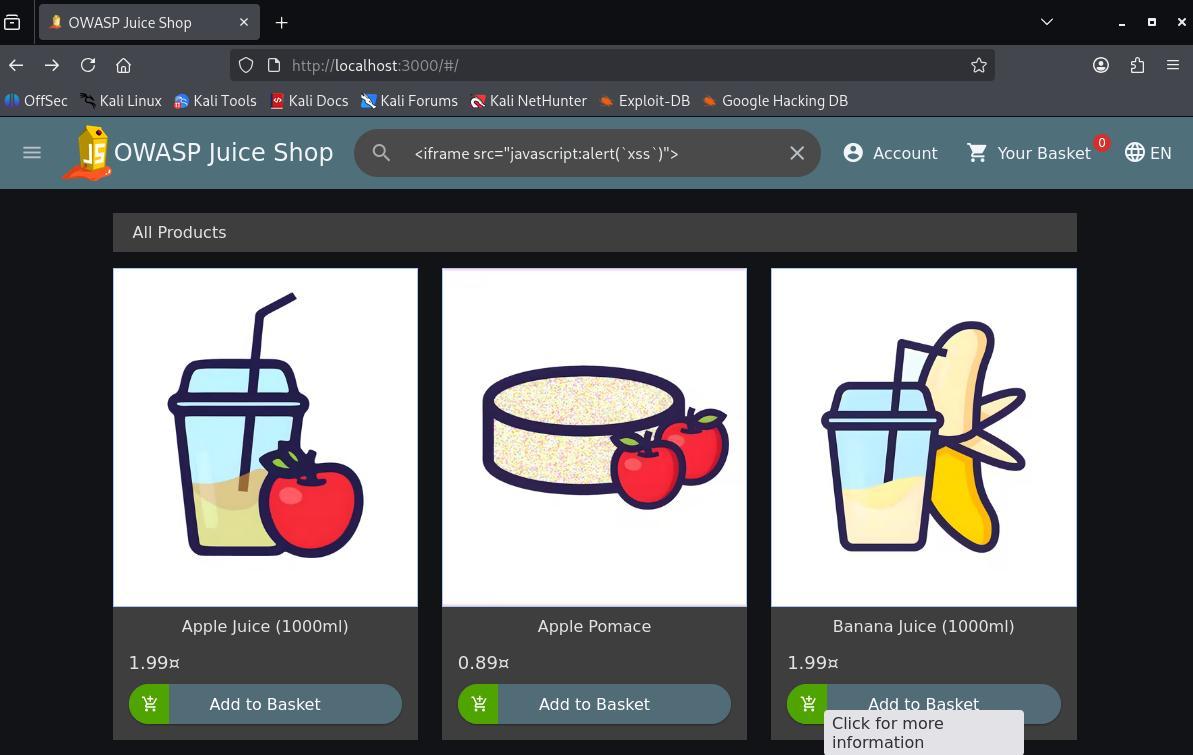
<iframe> payload in the search field — the app renders it instead of treating it as text.The fix is contextual output encoding and treating all input as data — never building markup from raw user strings.
Improper Input Validation
Client-side limits are only a convenience, not a control. A feedback form enforced a minimum star rating in the browser, but capturing the request and resending it with an out-of-range value (zero stars) — a value the UI would not allow — was accepted by the server. The lesson: validation has to be enforced server-side, because anything the client checks can be edited by the client.
Broken Authentication
This class is about weaknesses in how identity and sessions are handled — weak or default credentials, predictable sessions, and flows that let an attacker reach an account they shouldn't, such as logging in as the administrator.
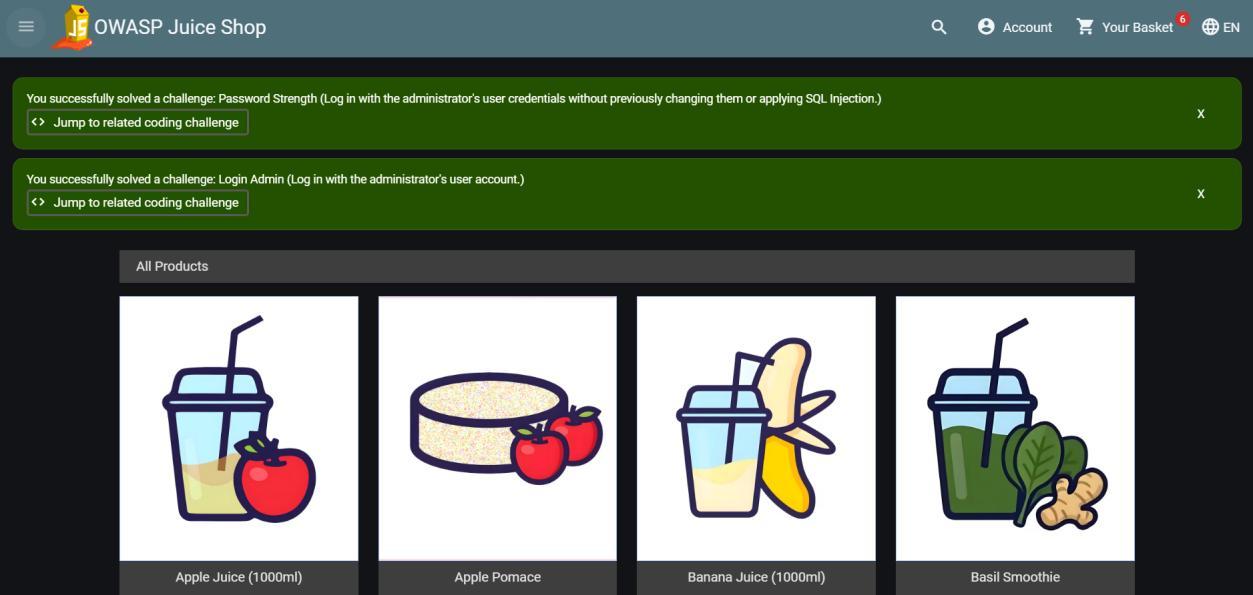
The defences are the familiar ones: strong password policy, MFA, no default accounts, and proper session management.
What I took from it
All three come back to one idea: never trust input, and enforce every rule on the server. Juice Shop is a great way to feel why each OWASP category matters by actually breaking it in a safe environment.