~/d4nnyX

← Writeups

IHack 2026

FSKM, UiTM Shah Alam · 30–31 Oct 2026 · 24 hours

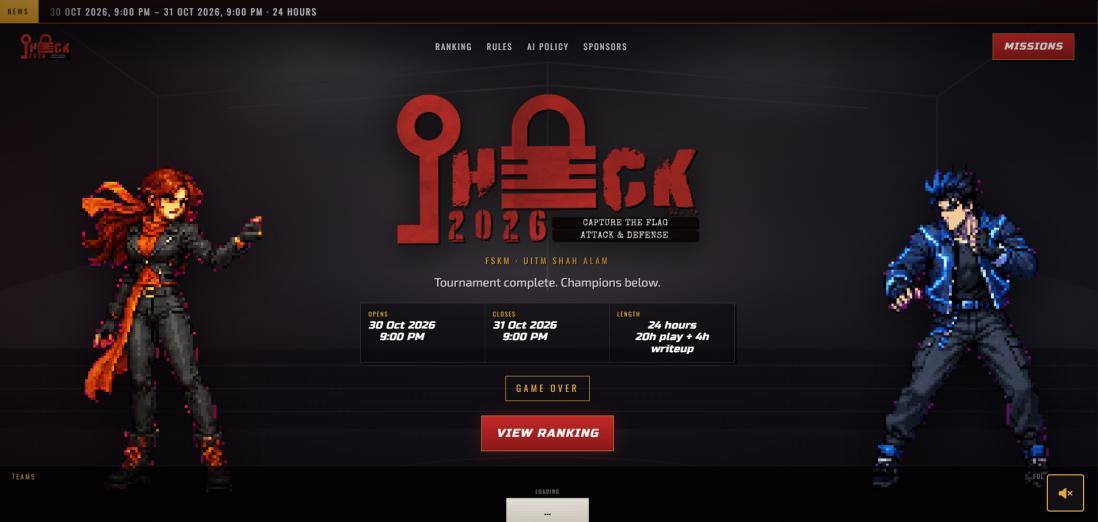
IHack 2026 CTF event site showing the Capture the Flag / Attack & Defense theme
IHack 2026 — Capture the Flag & Attack & Defense, FSKM UiTM Shah Alam.

IHack 2026 was a 24-hour jeopardy-style CTF run by FSKM at UiTM Shah Alam, with 20 hours of play and a 4-hour writeup window. Challenges were themed as fighting-game opponents you had to "KO" by submitting the correct flag.

These are my writeups for the challenges I solved, grouped by category: memory and network forensics, server-side template injection on the web, and an EVM smart-contract puzzle. Each page walks through how I approached it, including the dead ends.

Challenges

  • Forensics

    Feel My Wrath

    Carve a malicious CLAP audio plugin out of a VirtualBox memory dump, then reverse its flag-building routine in Ghidra.

    • Forensics
    • Volatility
    • Ghidra
    • Memory dump
  • Forensics

    ADUDU

    Recover a two-part flag from a PCAP: a blind-timing SSTI oracle for part one, and decrypting a TLS session with a weak RSA key for part two.

    • Forensics
    • Network
    • SSTI
    • TLS
    • RSA
  • Web

    North Line

    A Nuxt server island (.server.vue) is reachable directly and renders attacker-supplied props, turning a status chip into server-side template injection and RCE.

    • Web
    • Nuxt
    • SSTI
    • RCE
  • Blockchain

    Pen Rose

    An EVM lottery contract derives its secret number from public blockhash data and a hardcoded salt, so the winning guess can be computed off-chain.

    • Blockchain
    • EVM
    • Smart contract
    • Keccak256