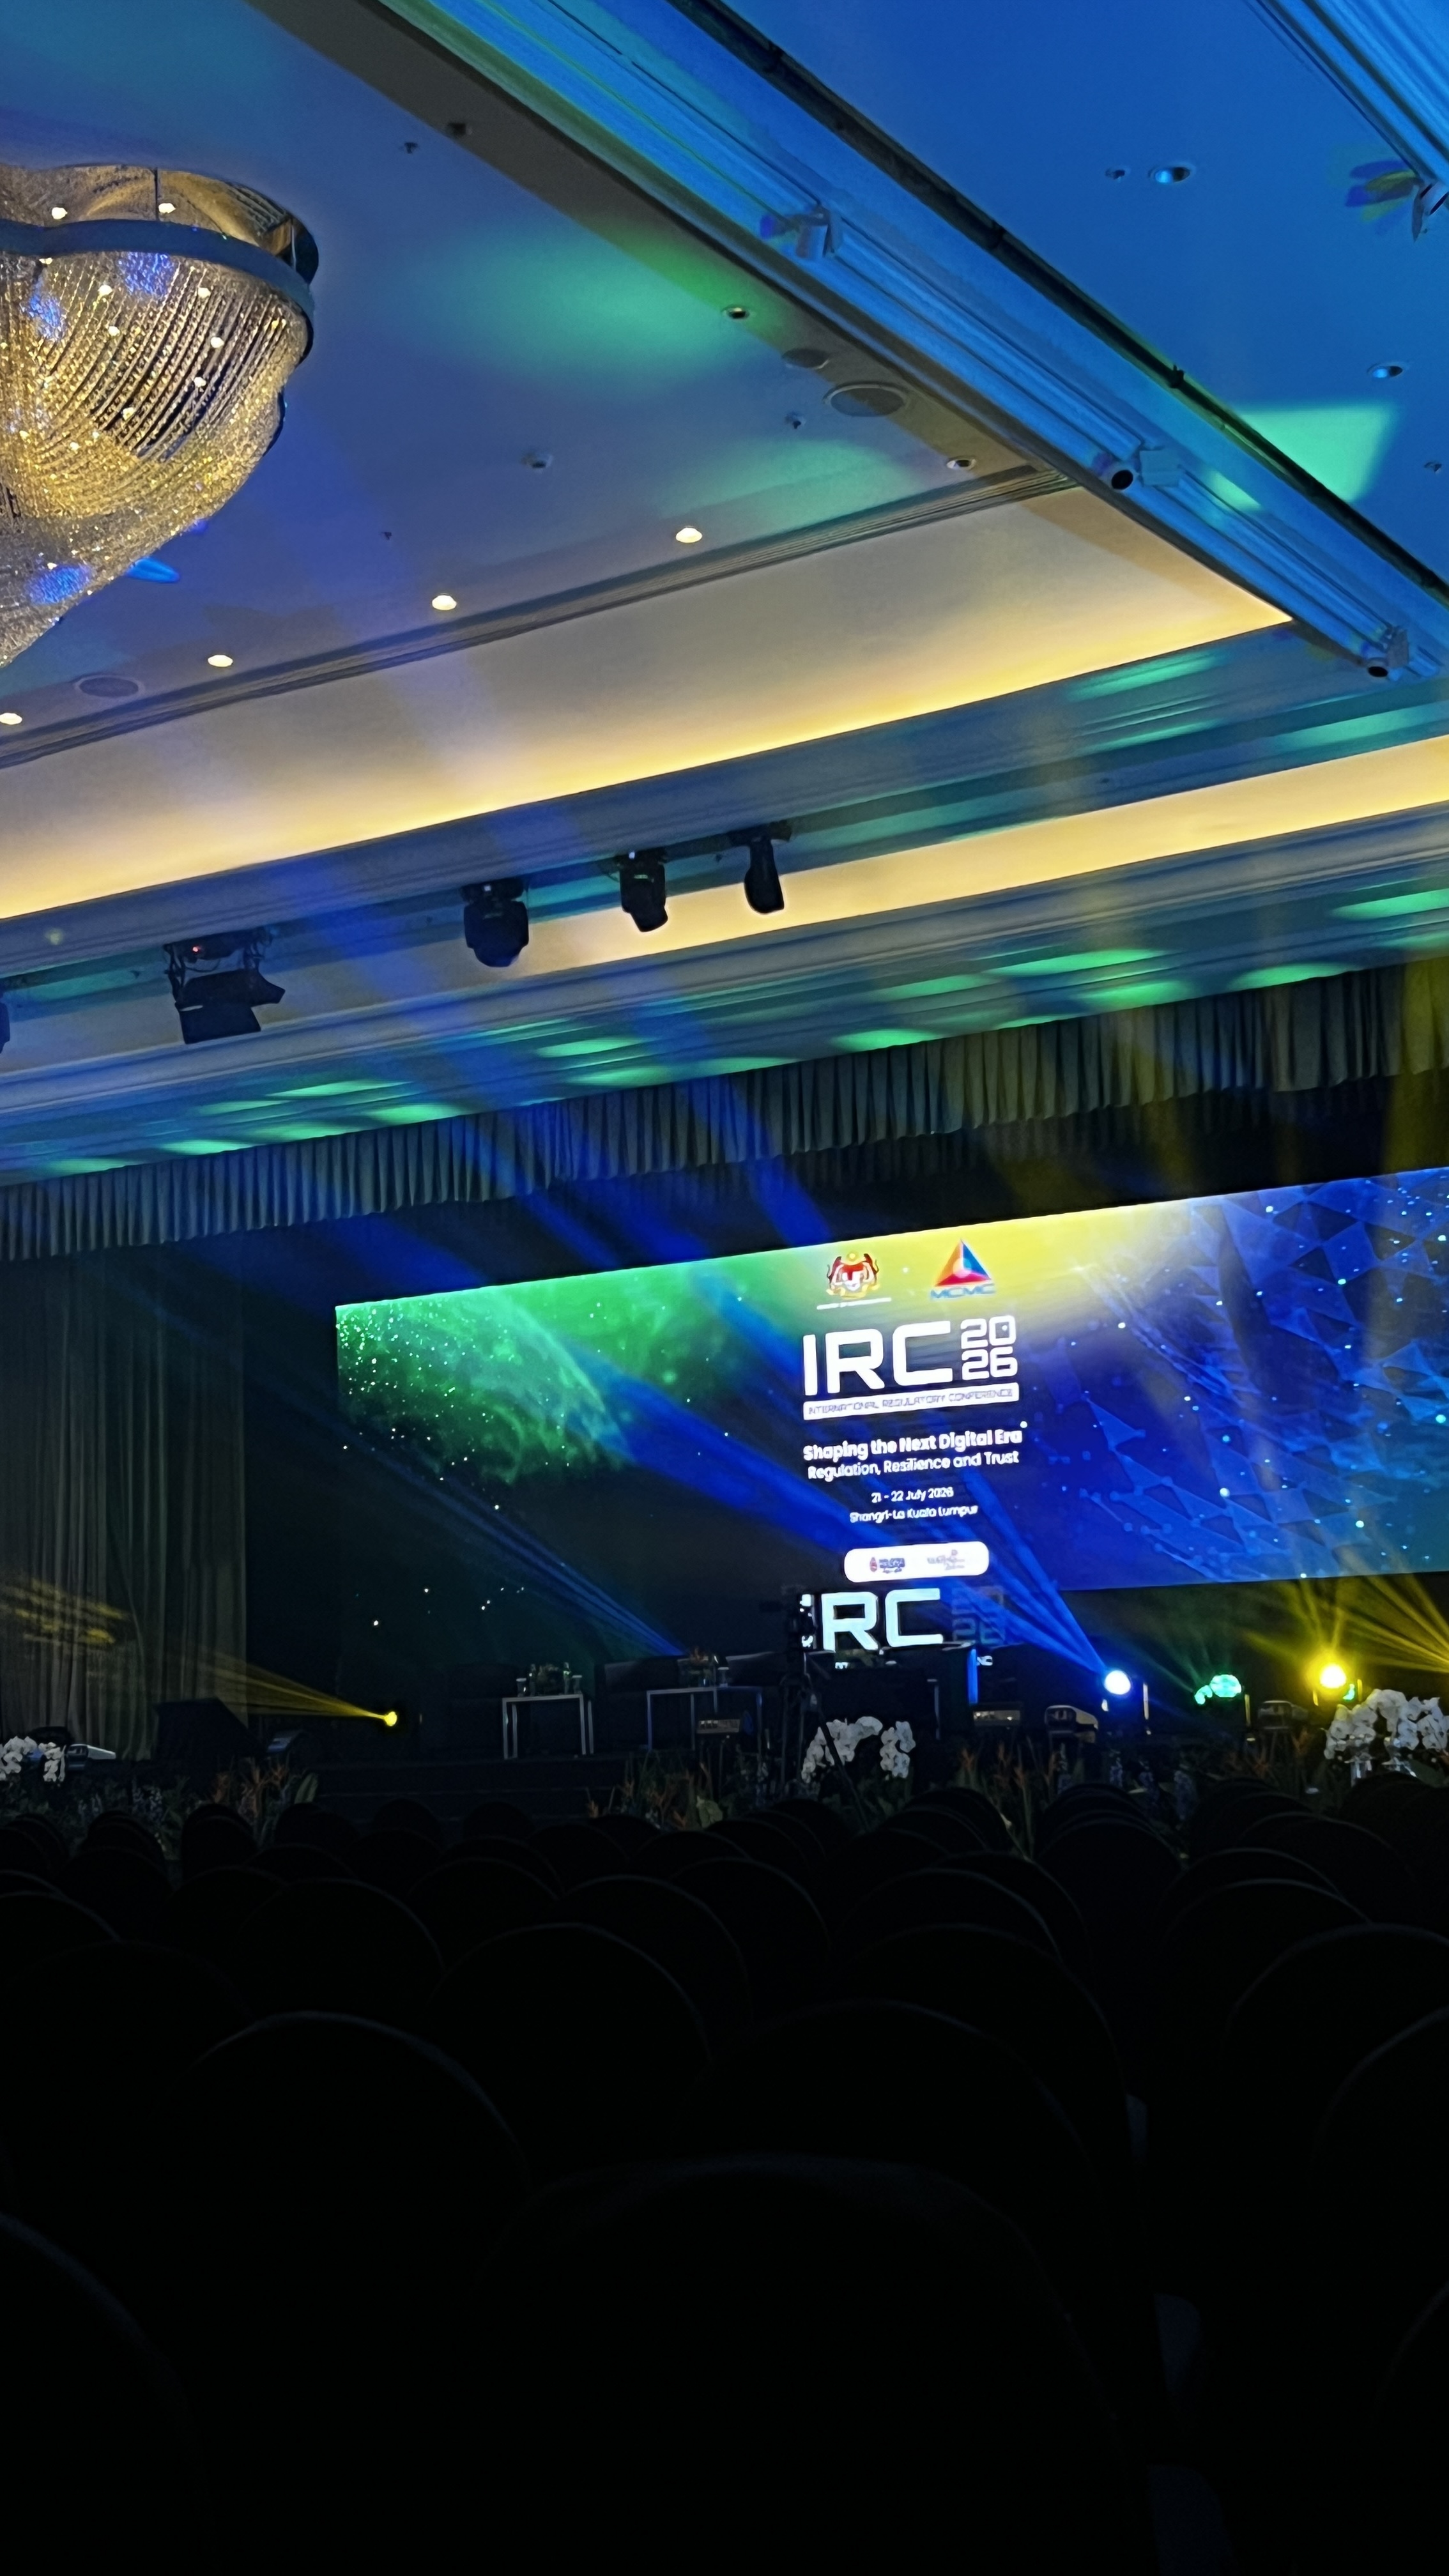
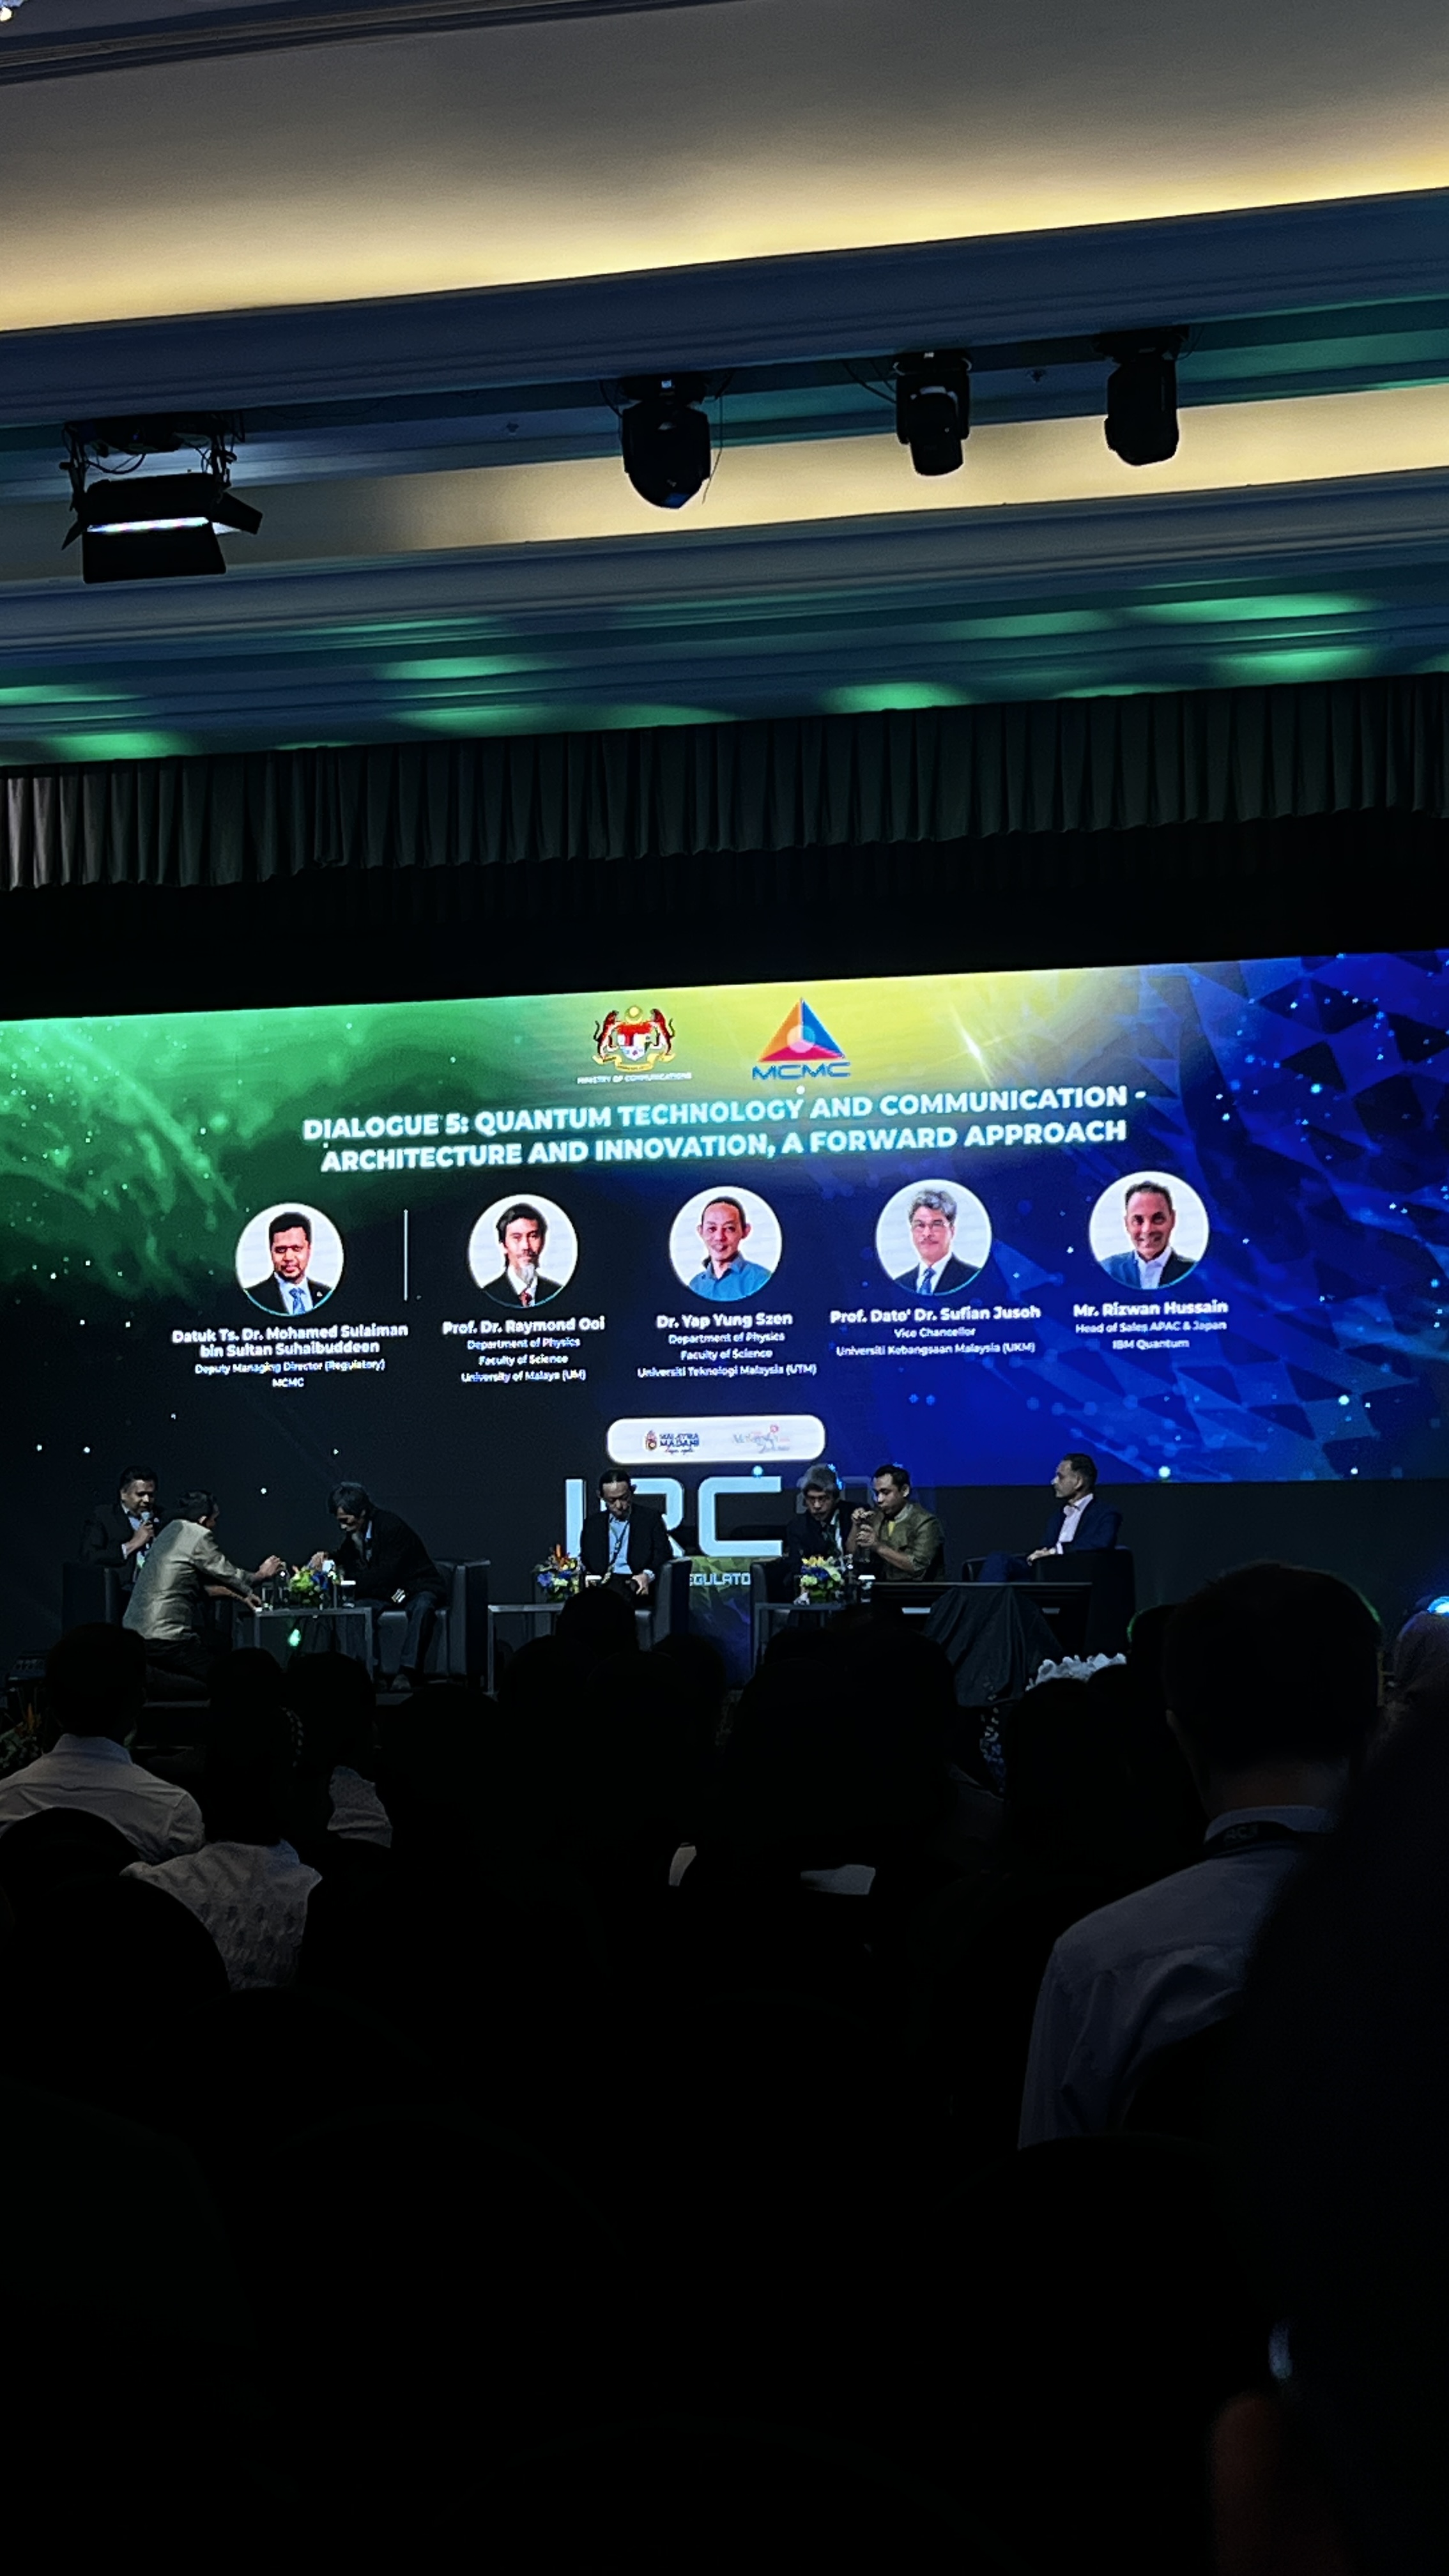
I attended the International Regulatory Conference, held at the Shangri-La Hotel. It sits at the opposite end of the field from a CTF — this is the policy, compliance and governance side, where the questions are about regulation and risk management rather than exploits.
Sitting in those rooms is a useful reminder that technical security lives inside a much bigger frame of law and governance. Knowing how that side thinks makes you a better consultant, not just a better hacker.