CPTS is a long road. The Hack The Box path takes you end-to-end through a real engagement — enumeration, exploitation, Active Directory, pivoting, privilege escalation and the reporting that ties it together — and it does not let you skip the fundamentals.
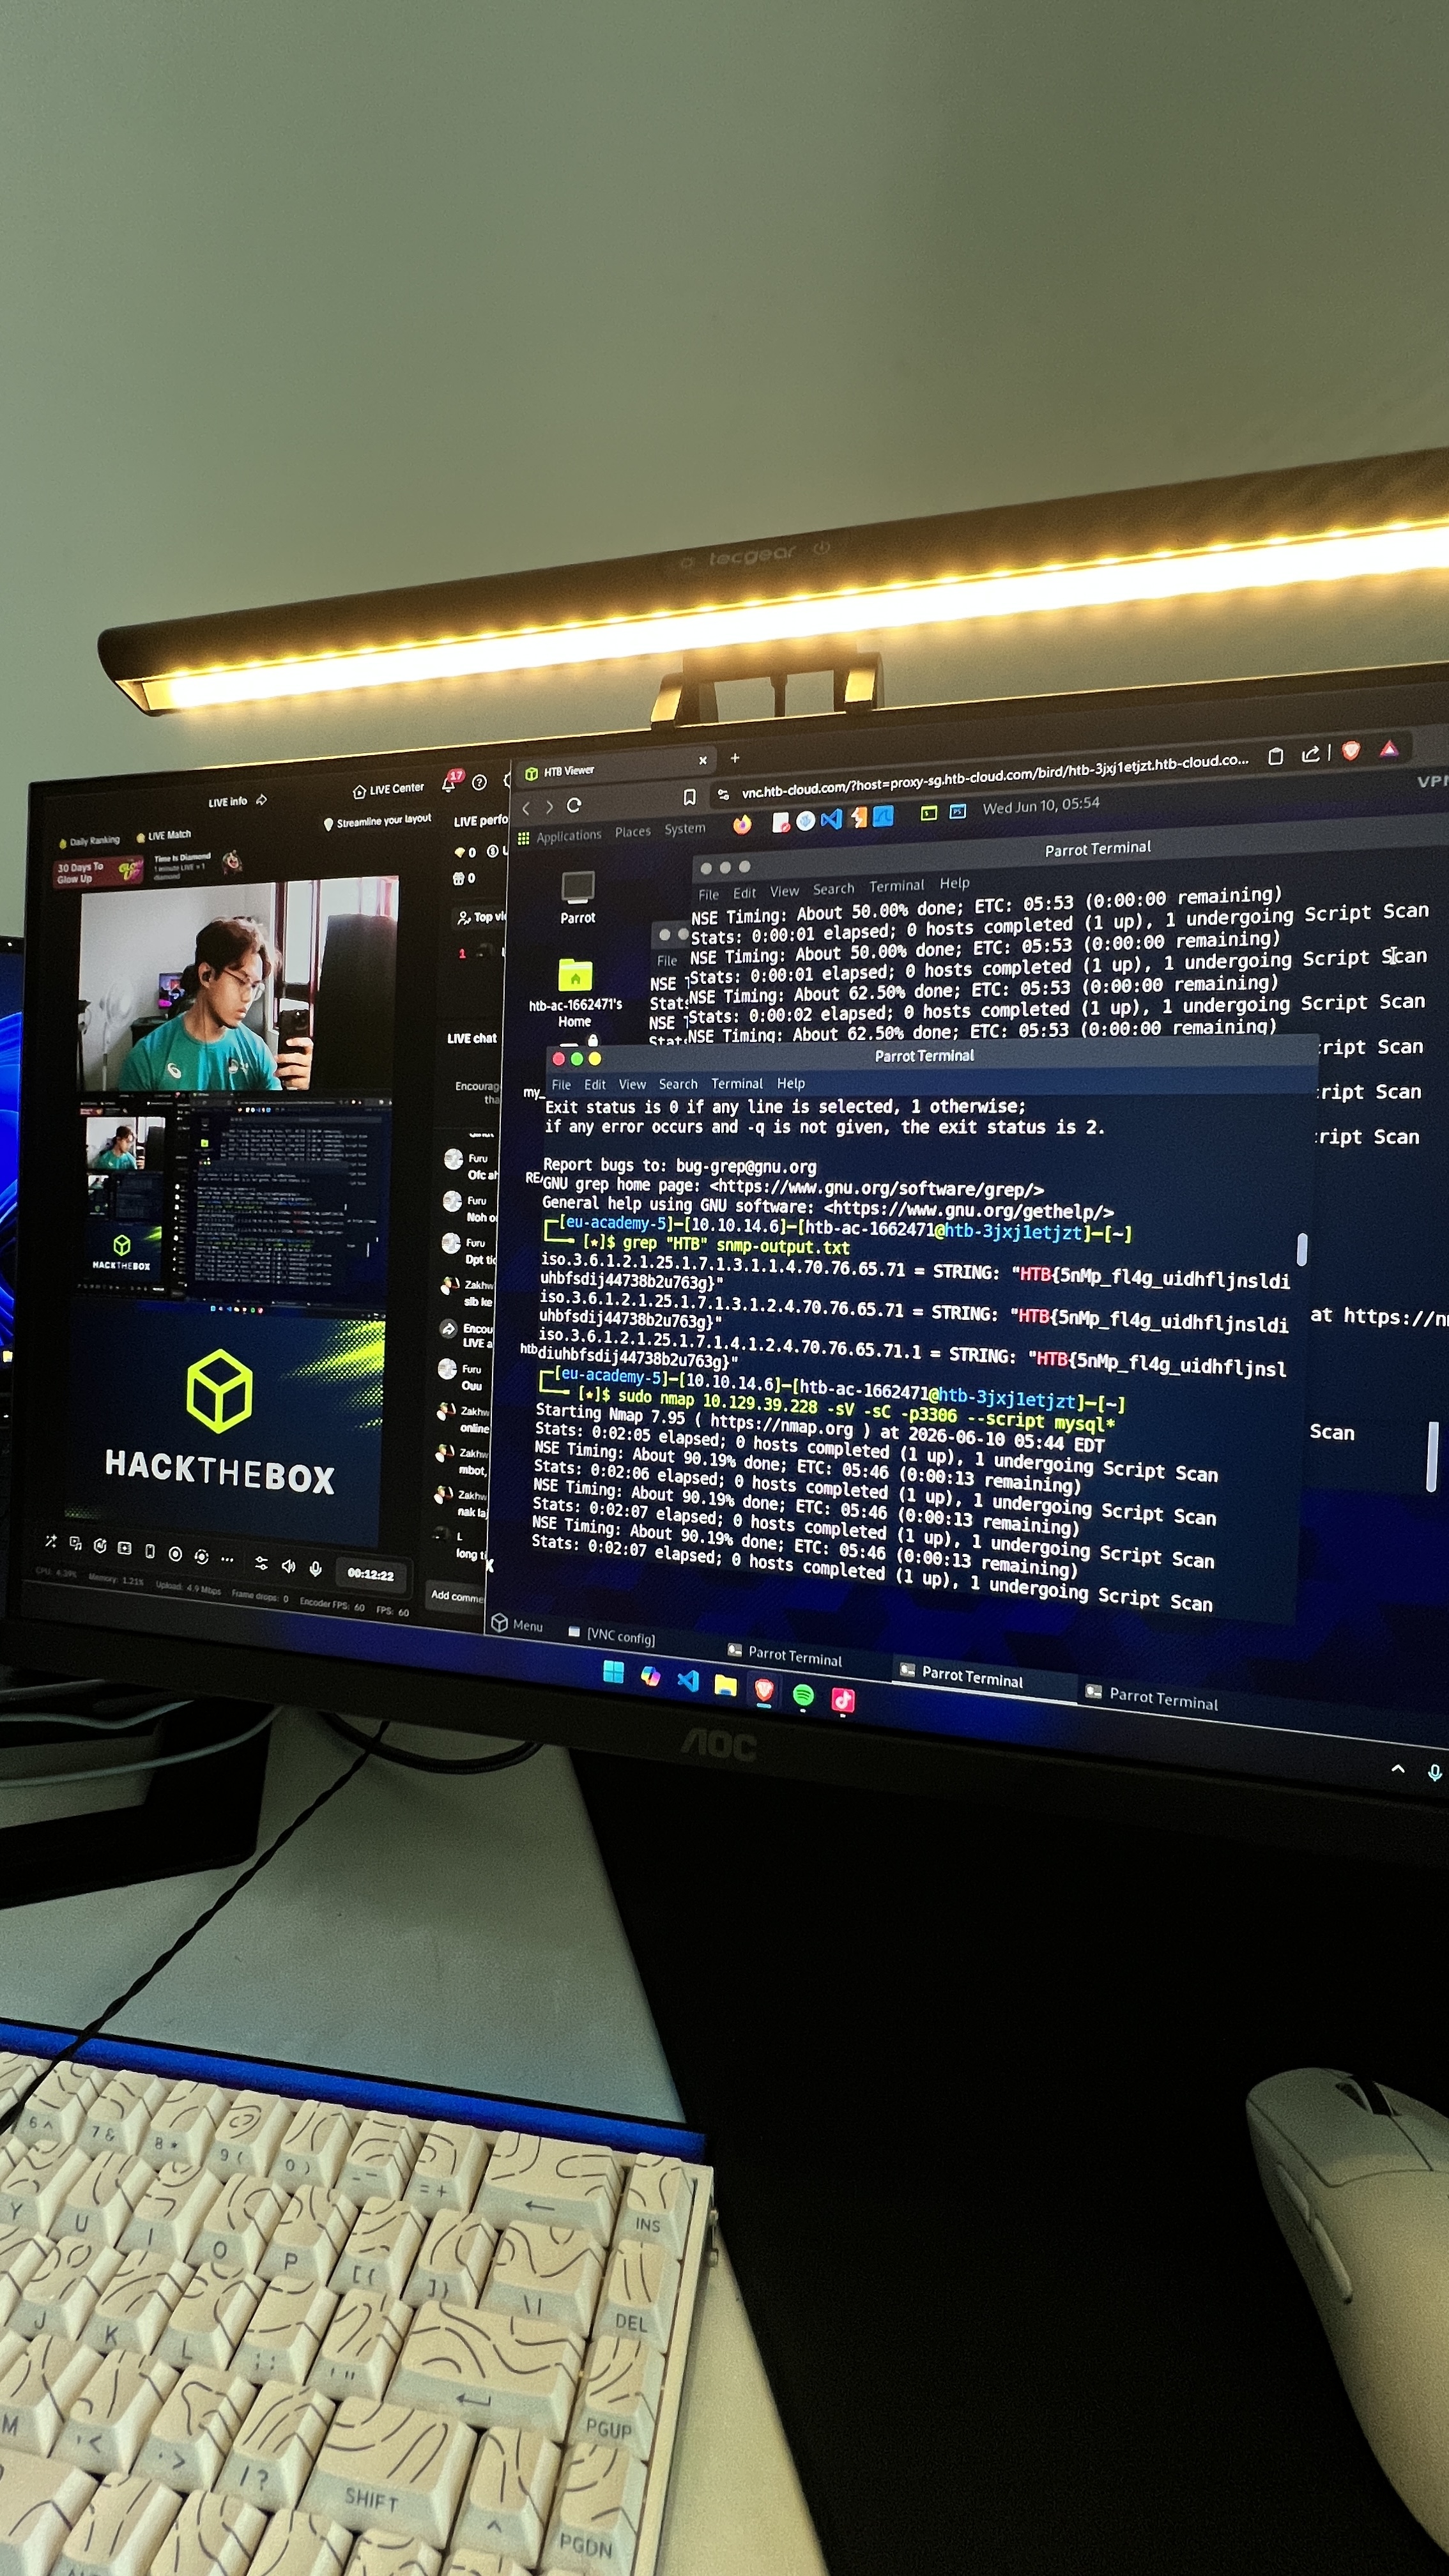
What stuck with me is how much of pentesting is methodology, not tricks: enumerate thoroughly, take notes you can turn into a report, and never assume a box is empty just because the obvious port is quiet. I've been writing up the modules as I go — you can read those CPTS notes here.